


When Accounts Become "Programmable": Restraint and Trade-offs from EIP-7702 and ERC-4337 to Native AA


- Core Viewpoint: Account abstraction is driving Ethereum accounts from a fixed private key model toward a programmable system, but behind the convenience lies a weakening of security certainties; wallets need to make prudent trade-offs between feature innovation and user asset security, and Native Account Abstraction (Native AA) may be the better long-term direction.
- Key Elements:
- EIP-7702 allows EOAs to delegate execution to smart contracts; a single authorization can alter the entire behavioral boundary of an account, with risk potentially spreading from a single transaction to all assets.
- ERC-4337 splits verification, execution, and Gas payment into multiple modules, creating a complex component chain that requires wallets to bear higher compatibility, maintenance, and security review costs.
- Although the traditional EOA experience is cumbersome, its account control relationships and verification rules are relatively certain—a security dividend that has long been underestimated.
- imToken has chosen to cautiously observe EIP-7702, halt new productization investment in ERC-4337, and shift toward Native AA research.
- The Ethereum Foundation has listed Native AA as a core direction under "Improve UX," with EIP-8141 (Frame Transactions) as a representative proposal, which remains in the Draft stage.
- Native AA aims to reduce dependence on peripheral infrastructure such as Bundlers and Relayers, lowering additional Gas overhead and architectural complexity.
If over the past decade the core responsibility of a crypto wallet has been managing private keys, signing transactions, and displaying assets, then going forward, wallets may need to take on much more.
Users no longer want to pay Gas separately for every transaction; they want a single signature to complete multi-step operations, to pay fees with stablecoins, and even to escape absolute reliance on a single private key through social recovery, session keys, and flexible permission management.
Behind all these demands points to the same technical direction: Account Abstraction (AA).
With the development of solutions such as EIP-7702 and ERC-4337, Ethereum accounts are gradually moving from a relatively fixed transaction execution model toward a more flexible, programmable account system.
But problems follow.
When an account can not only receive assets and sign transactions, but also execute complex smart contract logic, manage different levels of authorization, and even have a third party pay Gas on its behalf, is the user gaining more control, or introducing more security risks that they cannot understand?
1. From EOA to AA: Why do Ethereum accounts need to become "programmable"?
To understand account abstraction, one must first return to Ethereum's most fundamental account model.
For a long time, ordinary users have mainly used EOAs (Externally Owned Accounts), which are controlled by private keys. Users sign transactions with their private keys; the overall account structure is simple, the permission relationships are clear, and the transaction execution path is relatively easy to understand.
But this design also has some limitations in terms of experience.
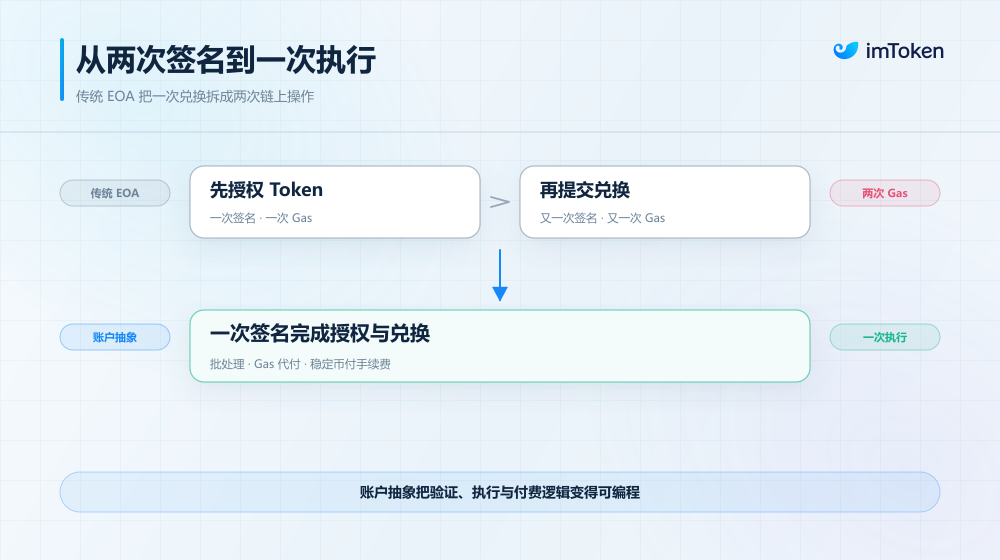
For example, if a user wants to complete a token swap on Uniswap, they often need to first approve the ERC-20 Token and then submit the swap transaction. This means two separate on-chain operations, two signatures, and two Gas payments.
If a user wants to pay Gas with USDT, or have an application bear the transaction fees on their behalf, a traditional EOA cannot directly accomplish these things through the account's own verification logic.
More importantly, whoever controls the private key essentially controls the entire account. It is difficult for users to directly set daily spending limits at the account level, restrict application permissions, or configure different signing rules for different use cases.
What AA attempts to change is precisely these limitations.
Its core idea is to make the account's verification, execution, and fee payment logic programmable, so that users no longer have to rely solely on a fixed set of private key signing rules, but can define as needed how the account verifies identity, executes operations, and pays fees (Further reading: "The $3.35 Billion 'Account Tax': When EOA Becomes a Systemic Cost, What Can AA Bring to Web3?")
Ultimately, the greatest value of account abstraction is that it enables wallets to perform operations that were difficult to achieve in the past, but from a security perspective, this is exactly where the problem lies.
After all, in the past users only needed to focus on whether they were signing a correct transaction and whether the signature was being maliciously exploited; in a smart account system, however, a seemingly ordinary authorization may involve account execution code, permission modules, third-party payment services, and collaboration among multiple different roles.
What the user sees may be just one confirmation, but what actually happens may be a change in the entire account control logic.
From this dialectical perspective, traditional EOA accounts do seem cumbersome in terms of experience, but they have long provided the entire crypto world with a security dividend that is easily underestimated—the relative determinism of account control relationships and verification rules.
Users hold private keys and directly sign to authorize transactions. Although private key leakage, malicious approvals, and phishing risks always exist, the account itself does not need to load complex smart contract logic to adjudicate the verification and execution of each transaction.
AA breaks this single structure.
2. The Other Side of AA's Convenience: When Accounts Lose "Determinism"
Once accounts have stronger programmability and batch execution capabilities, what users mistakenly sign may no longer be merely an approval for a certain token, but may also involve account delegation, execution modules, and broader operational permissions. Once these permissions lack clear boundaries, risk can quickly spread from a single transaction to the entire account.
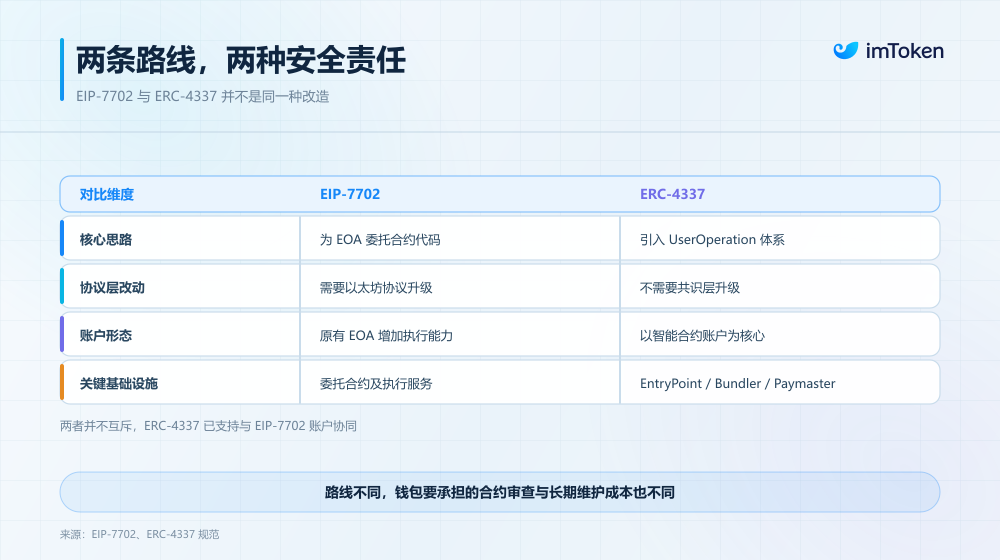
This is also why, under the AA approach, although EIP-7702 and ERC-4337 both improve the account experience, the risk exposure they create at the wallet security level is entirely different—it should be noted that the two are not completely mutually exclusive solutions; the latter has already incorporated compatibility support for the former. They are discussed separately here mainly to understand their respective typical account implementation methods and the different challenges they face at the product security level.
1. EIP-7702: One Authorization May Change the Entire Account's Behavioral Boundaries
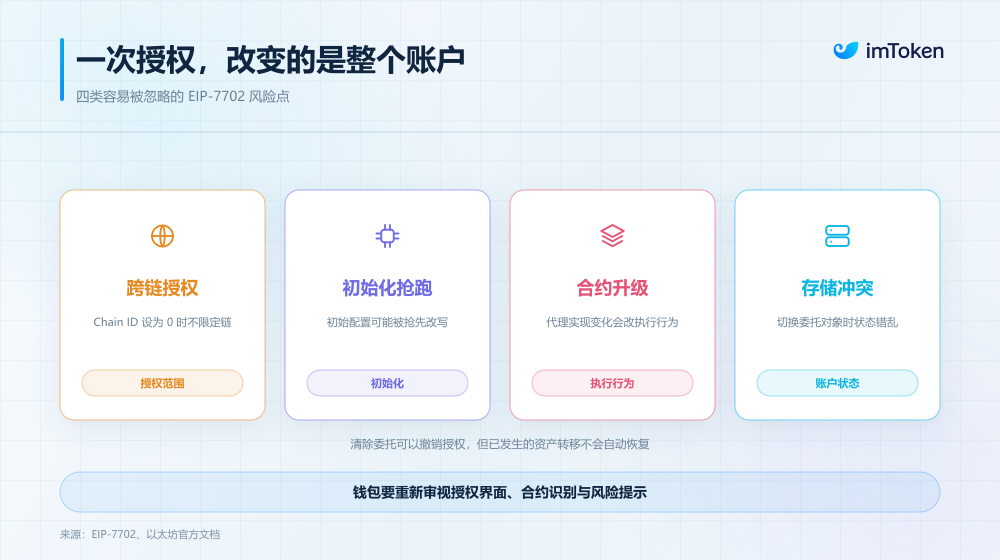
The security proposition most worth watching in EIP-7702 is account delegation.
By signing an authorization message, an EOA with originally fixed rules can delegate itself to a deployed smart contract address and directly run according to that contract's code.
A fully audited contract with strict permissions can indeed grant existing accounts capabilities such as batch transactions and Gas sponsorship at low cost; but once delegated by mistake to a malicious contract or a contract with serious vulnerabilities, the risk will penetrate directly to the account's assets.
This differs markedly from ordinary DApp interactions. In DeFi applications, mistakenly signing a malicious approval usually puts risk first within the permission scope defined by the specific Token, approval amount, and target contract; but if the user grants an unlimited allowance, the loss can likewise be very severe.
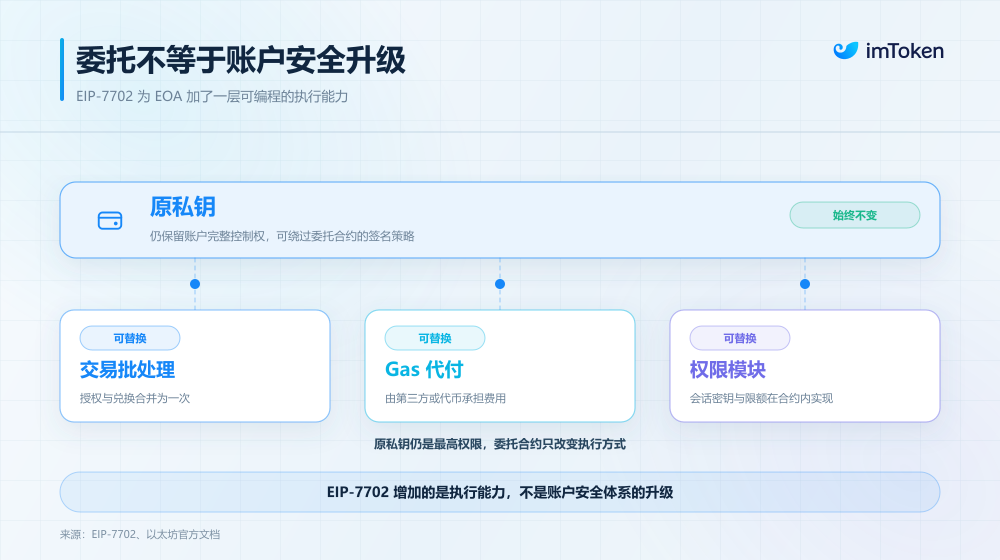
In the EIP-7702 delegation scenario, the authorized code runs directly in the account context. If the delegated code has unrestricted asset transfer or contract call capabilities, the risk may expand from a specific token approval to the entire account, affecting ETH, various ERC-20 assets, and subsequent transaction operations.
However, EIP-7702 does not strip the original private key of control over the EOA. Even if the user delegates the account to a contract with multisig logic, the original private key can still directly control the account, bypassing some of the signature policies set by the delegated contract.
In other words, adding smart contract execution capability to an EOA is not equivalent to automatically tightening the permission constraints on the underlying private key. Likewise, although users can revoke delegation by re-authorizing an empty address, the revocation action cannot roll back asset transfers and on-chain state changes that have already occurred.
This also determines that wallets must never treat EIP-7702 simply as a new signing method. They must rebuild an entire security defense line around the authorization interface, contract identification, permission display, delegation revocation, and risk control prompts.
2. ERC-4337: Risk Is Not Only in the Account Contract
Unlike modifying existing EOAs, ERC-4337 splits account verification, transaction execution, and Gas payment into independent modules, giving developers room for flexible combination, but also burdening wallets with more complex component management costs.
From creation to on-chain inclusion, a UserOperation usually goes through an entire collaboration chain: the wallet generates the operation and completes signing → the Bundler receives the UserOperation and performs off-chain checks through EntryPoint's simulated verification logic → the Bundler packages operations that pass verification and submits them to the on-chain EntryPoint → the EntryPoint again executes the verification logic of the account and the payer, and after passing, executes the actual operation.
If fee sponsorship is involved, a Paymaster also needs to participate in verification and fee settlement; if a new smart account needs to be created, it may involve the deployment and initialization of a Factory contract.
As the number of components surges, wallets must simultaneously deal with more complex compatibility, operational reliability, and security review challenges. In addition, because a smart account is not simply a feature switch added to an existing EOA, its contract implementation, signature verification method, module configuration, EntryPoint version, and supporting infrastructure will all profoundly affect its future evolution path.
As Ethereum gradually moves toward Native AA, how existing accounts remain compatible with new protocols, how original permissions are migrated, and how account addresses and assets maintain continuity all need to be considered in advance.
Ultimately, for wallets, the real cost of adopting a technology today is never just development and launch, but also continuous maintenance and support for years to come.
3. From Application-Layer AA to Native AA: Restraint and Trade-offs in the Technical Path
Having seen clearly the security complexity and maintenance costs behind the two paths, how wallet products should choose is actually becoming clear: whether to adopt a technology cannot depend only on how many features it can deliver, but must also weigh technical maturity, the user cognitive threshold, and the long-term sustainability of the architecture.
Taking imToken's practice in account abstraction as an example, after evaluating multiple paths the team made a clear trade-off—maintaining a cautious, observant stance on EIP-7702 while stopping new productization investment in ERC-4337, and gradually shifting research focus toward Ethereum native account abstraction (Native AA).
First, regarding EIP-7702: the technical capability is worthy of recognition, but there is no rush to fully productize it.
To be realistic, EIP-7702, which has already entered the Ethereum mainnet, can give traditional accounts capabilities such as batch transactions and Gas sponsorship, and its engineering design and experience improvements are evident to all.
But before it is truly opened to a large number of ordinary users, several core preconditions are still not fully mature: Can users intuitively understand the difference between "account delegation" and ordinary signing? Has the industry formed a reliable consensus on security review, permission display standards, and emergency rescue for delegated contracts?
These issues are especially important in the EIP-7702 scenario. If an ordinary user cannot clearly understand what the authorization they sign means, then even if the technology itself can implement complex security policies, it may not truly improve the user's security level.
Therefore, imToken chooses a cautious, observant approach to EIP-7702 and is not in a hurry to fully introduce it into its product system, slowly waiting for the relevant implementations, permission management mechanisms, and industry practices to undergo longer-term testing. This is also intended to establish a more reliable security boundary between technical capability and users' actual ability to understand.
By contrast, ERC-4337 has already proven the feasibility of smart accounts through extensive production practice and has accumulated valuable experience for the industry.
But viewed from a longer technology cycle, when Ethereum's development direction is gradually pointing clearly toward native support at the protocol layer, continuing to expand productization investment around an application-layer account abstraction architecture requires re-weighing the ongoing maintenance costs of peripheral infrastructure, as well as the compatibility and migration costs that may arise in the future when connecting with native protocol capabilities.
Therefore, imToken's decision to stop new ERC-4337 productization investment and gradually shift its research focus to Native AA is not a denial of ERC-4337's technical value. Rather, it is to avoid continuously stacking complexity onto the existing architecture and to devote limited engineering and security research resources more to the direction of native account abstraction with long-term development potential.
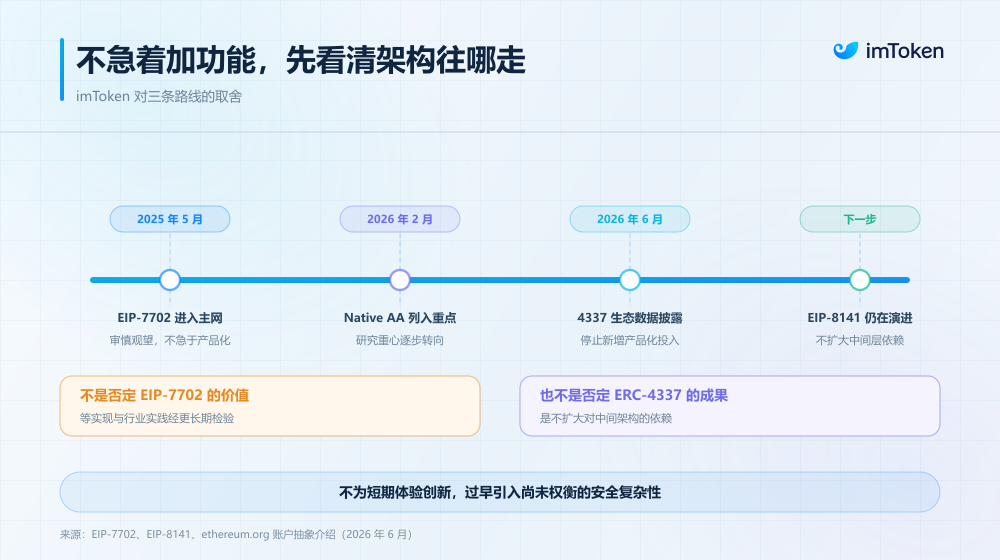
This choice also echoes Ethereum's own protocol evolution direction.
In February 2026, when the Ethereum Foundation updated its protocol development priorities, it explicitly listed Native AA as one of the core work items in the "Improve UX" direction. Its long-term goal is to make smart contract wallets the default account form while reducing dependence on peripheral infrastructure such as Bundlers and Relayers, as well as the additional Gas overhead they generate.
Among specific technical proposals, EIP-8141 (Frame Transactions) is currently one of the representative directions worth watching. It attempts to split transaction verification, fee payment authorization, and actual operation execution into different stages, allowing accounts to define verification rules and payment methods through their own logic, providing a new implementation path for protocol-layer native support of smart accounts.
Of course, EIP-8141 is still in the Draft stage, and there is still some time before formal deployment and large-scale application. Native AA also does not mean security risks will automatically disappear; account verification code still requires rigorous auditing, and new transaction verification and fee payment mechanisms likewise need to be fully tested.
But from a long-term architecture perspective, compared with continuously adding features to existing intermediary layers and maintaining complex compatibility relationships, laying out the security architecture in advance on a more native and unified protocol foundation is clearly more in line with imToken's consideration of long-term wallet security.
Final Thoughts
From the earliest private key signatures to today's batch transactions, Gas sponsorship, session keys, and smart accounts, account abstraction is continuously expanding the capability boundaries of crypto wallets.
But no matter how the technical form evolves, the most essential value of a wallet has never changed: it must not only enable users to complete more operations, but also ensure that in every interaction users always clearly understand what they have authorized and who actually controls their assets.
Returning to specific product practice, this is also the underlying logic behind imToken's recent clear trade-off in its account abstraction technical path—maintaining a cautious, observant stance on EIP-7702 while waiting for a more long-term and stable protocol and security paradigm; at the same time stopping new productization investment in ERC-4337 and gradually shifting its research focus to Native AA.
This is not abandoning account abstraction innovation. On the contrary, it is a pragmatic choice made based on user asset security, technical maturity, and long-term architectural evolution—not prematurely converting the complexity of protocols still in a transitional period into asset risks and migration costs for ordinary users.
Ethereum's account evolution is a long run. On the road to native account abstraction, carefully assessing technical maturity and security risks may be more important than pursuing rapid feature rollout.





