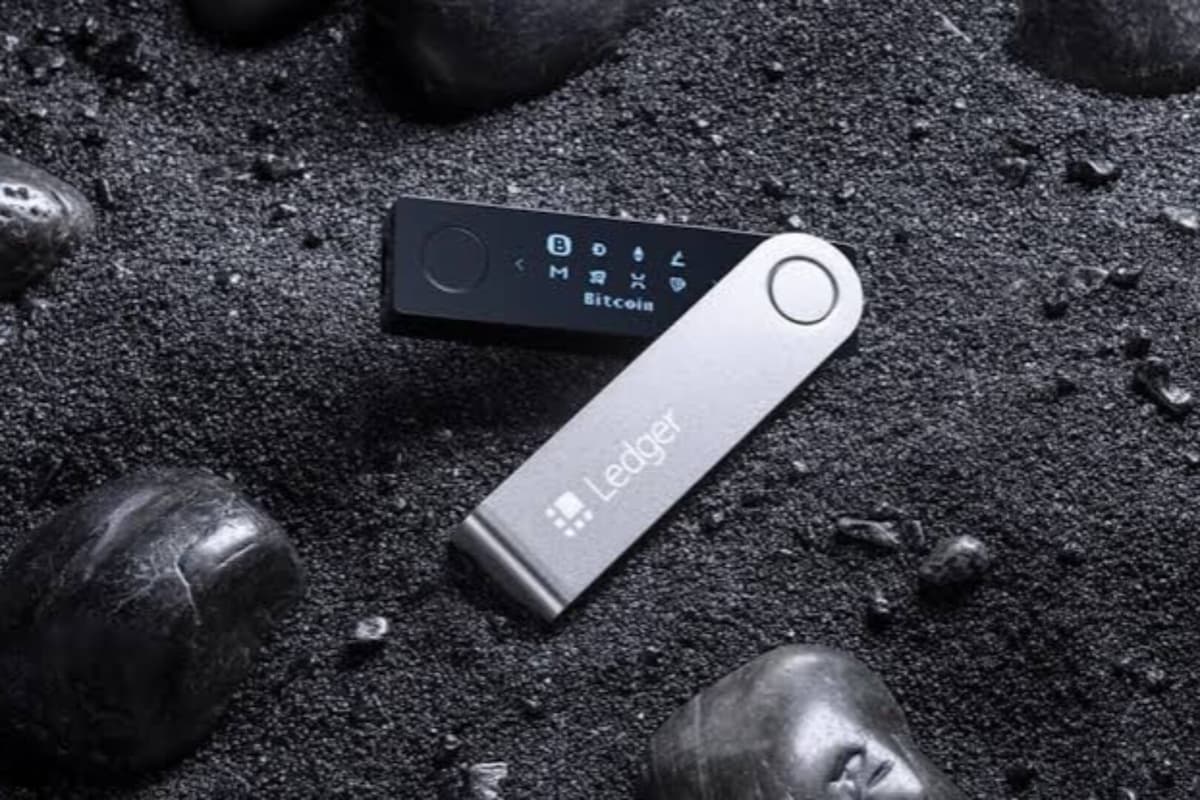
Odaily reports that SlowMist's Cos posted on X platform stating that the strongly correlated cases he is following up on include the Ledger Flex; in addition to the widely known Ledger Nano X, Ledger's mainstream series may have been tampered with at its reseller CryptoBills.


Odaily: According to a post by Bitcoin News on X, Ledger stated that the number of affected devices is limited, and as of now, all confirmed cases related to the October 9 fund theft incident involve devices sold through Southeast Asian distributor CryptoBilis. Ledger's internal systems and direct sales channels were not affected. CryptoBilis has suspended all hardware wallet sales, and Ledger is cooperating with law enforcement and contacting affected customers. Ledger advises CryptoBilis buyers not to initialize unused devices; users who have already completed initialization should transfer their funds to a new wallet using a new seed phrase. The investigation is still ongoing.
Odaily reports, according to monitoring by Bitcoin News, @0xJohannes stated that a Ledger hardware wallet purchased from an official European reseller several weeks ago was found to contain an unauthorized spy implant device. Suspicious wiring not present in genuine Ledger hardware was discovered inside the device, indicating it may have been physically tampered with before being sold. The implant appears to be an older version, as newer versions typically conceal the components behind the screen. Funds in the affected device have not been stolen thus far. Suspected cases have currently been reported in Asia, South America, and Europe. If the original secure element remains intact, Ledger's Genuine Check software cannot detect unauthorized physical modifications.
Odaily News: According to on-chain detective Specter's monitoring, between October 9 and 10, attacker addresses associated with the CryptoBilis Ledger hardware wallet incident deposited 2,990.3 ETH, worth approximately $7.45 million, into Tornado Cash.
Monitoring shows that the attacker had previously withdrawn funds to 14 addresses, then bridged them cross-chain to ZEC via NEAR Intents and conducted privacy-enhancing processing. Specter stated that the attacker partially reused previous deposit addresses to submit withdrawal transactions, while some other withdrawal transactions were initiated by wallets linked to addresses that paid gas fees during the fund theft, thereby linking the deposits to the withdrawal activity.
Currently, the attacker is still continuously moving and concealing the related funds. The previous CryptoBilis incident involved supply chain risks related to Ledger hardware wallets. Ledger has stated that it is investigating and has reminded affected users to pay attention to device security.
Odaily News: Crypto analyst Darkfost posted that following the security incident involving Ledger reseller CryptoBilis, other potentially related reseller names have emerged in community discussions, including some Lazada merchants.
Darkfost stated that the full scope of the incident remains difficult to confirm. Although Ledger has confirmed a connection to the CryptoBilis incident, it is still unclear whether CryptoBilis is the only affected reseller. He compiled a list of potentially risky Ledger resellers, noting that due to their regional proximity, there is a possibility that their supply chains were compromised simultaneously. However, Darkfost emphasized that these assessments are speculative and have not yet been confirmed.
Darkfost advised that if users have purchased Ledger devices from the relevant resellers within the past 6 months, they may consider moving their assets to other secure devices before the investigation concludes. He also noted that users can refer to a guide published by security researcher MagicalTux to check their Ledger devices for signs of tampering.
Odaily News: CryptoBilis has suspended all branded hardware wallet sales and shipments across all physical stores and online channels in Malaysia, the Philippines, and Indonesia, with physical stores temporarily closed. The company stated that this move is to protect customers during the investigation of the Ledger security incident and an independent expert review of internal processes. Undelivered orders will be proactively handled by customer service, and users who have already purchased Ledger devices should follow security guidelines. CryptoBilis expects to announce further developments within three business days.
Odaily reports that former Mt.Gox CEO Mark Karpelès stated that a Ledger hardware wallet he purchased from Malaysia was found to contain a suspicious module with a SIM card chip built in. The module was hidden in the screen padding area, and the device's outer packaging was intact.
Slow Mist Chief Information Security Officer 23pds analyzed that attackers may have connected the malicious module to the screen data cable to record the words displayed when the device generates seed phrases, and then used LTE or eSIM to transmit the data externally.
23pds pointed out that the secure element of a hardware wallet is mainly used to prevent private keys from being directly read, but it cannot prevent malicious hardware from capturing screen display content. Currently, the related attack mechanism remains a technical speculation and still awaits further verification.
According to monitoring by Galaxy's head of research, in the Ledger CryptoBillis attack incident, approximately $72.9 million remains in addresses controlled by the attacker, involving Bitcoin, Ethereum, and USDT; $3.1 million entered Tornado Cash, while the remaining funds have been bridged across chains, swapped, or layered and transferred through relayers.
According to Odaily, citing Galaxy's head of research, the losses from the Ledger CryptoBillis supply chain attack currently amount to 213.42 BTC, approximately $17.7 million. Of this, 92% of the funds were held for less than 90 days at the time of consolidation, while some funds were held for longer periods. All traced Bitcoin remains unspent and is stored in 3 consolidation addresses.
Odaily News: According to monitoring by Galaxy's head of research, the Bitcoin losses caused by the Ledger cryptocurrency supply chain attack currently amount to 213.42 BTC, valued at $17.7 million. Of this, 92% of the funds were transferred in less than 90 days ago, while some funds were transferred even earlier. All Bitcoin traced so far remains unspent and is held in 3 aggregation addresses.
Odaily reports that Bitcoin News posted on X platform stating that corporate records for Malaysian hardware wallet distributor CryptoBilis show that, as of August 3, an individual named Jiaming, with a registered address in Heilongjiang Province, China, holds 100% of the company's shares. The company's former co-founder confirmed that CryptoBilis completed its acquisition in March, with the original owner withdrawing from all operational, managerial, and administrative roles. The founder has been unable to learn about the company's operations since the handover but still assists with event coordination. This information emerged during an investigation into a suspected supply chain attack on Ledger hardware wallets, where affected devices were implanted with hidden components that could steal seed phrases; there is currently no conclusive evidence linking the change in CryptoBilis ownership to the compromised wallets.
According to Onchain Lens monitoring, the suspected hacker behind the reported $90 million Ledger reseller incident has deposited 430.2 ETH, worth $1.07 million, into Tornado Cash through 4 wallets. After Tether froze the related funds, the hacker swapped USDT for USDD through SUN.io and USDD's PSM, with some funds also flowing into Binance hot wallets.
The hacker's wallet tracked by Arkham currently holds a total of $70.6 million in assets, including 11,406 ETH worth $28.35 million; 213.371 BTC worth $17.65 million; 13.646 million USDD worth $13.65 million; and 10.909 million USDT worth $10.91 million. Onchain Lens is calling on Binance to investigate these transfers and freeze accounts associated with the stolen funds as soon as possible.
Odaily News — According to monitoring by Bitcoin News, former Mt. Gox CEO Mark Karpelès may have inadvertently triggered a coordinated transfer of funds across multiple wallets after publicly disclosing physical tampering with Ledger devices equipped with hidden surveillance implants. On October 8, Karpelès warned that counterfeit or tampered Ledger devices with hidden SIM cards were being sold on the market, and these SIM cards were capable of transmitting stolen seed phrases. The implants were reportedly able to intercept data sent to the device screen, thereby capturing the recovery phrases displayed to users during wallet setup. Such devices could allegedly still pass Ledger's official genuine product verification, because the original secure element remained intact and the verification process was unable to detect unauthorized physical modifications. One emerging speculation is that attackers collected seed phrases from affected devices and waited to simultaneously transfer funds from multiple wallets. Karpelès's warning reportedly received approximately 90,000 views, which may have made the attackers aware that their operation had been exposed and prompted them to move the stolen funds. Karpelès stated that one affected Ledger device he examined came from Malaysia, was packaged in intact shrink wrap, and had an implant hidden beneath the screen. The suspected attack path is currently a compromised hardware supply chain rather than a vulnerability in cryptographic algorithms. The connection between Karpelès's warning and the subsequent wallet fund transfers has not yet been confirmed, nor has it been verified whether the same batch of implants was responsible. If the relevant circumstances are confirmed, the incident would demonstrate that even if a device is certified by the manufacturer, compromised hardware can still undermine users' self-custody security.
According to Lookonchain monitoring, an address bought 80 BTC for approximately $5.2 million 4 months ago at a purchase price of about $65,000 per coin, and at one point had a profit of $1.38 million. A week ago, the address purchased a Ledger device from reseller CryptoBillis and deposited all 80 BTC into the device. All assets have now been lost.
According to Lookonchain monitoring, some users who purchased Ledger hardware wallets have had their funds stolen, with all affected devices purchased from reseller CryptoBillis, and reported total losses approaching $90 million. Among them, a user with an address labeled TY24Ya purchased the device three weeks ago and deposited 7 million USDT into it, but approximately 10 hours ago the entire amount was stolen, potentially the largest single loss in this incident.
According to MistTrack monitoring, Odaily reports that Tether has frozen a large amount of USDT on addresses related to the Ledger user fund theft incident. The losses from this incident have approached $90 million, and some affected users have contacted MistTrack for assistance, with the team currently following up. Previously, Ledger stated it was investigating the theft of user funds related to Southeast Asian distributor CryptoBillis.